AI Agents Can Help With Client Email, but They Should Not Send on Their Own
By Loïc Guyon, operator of Pitstop · Updated · 8 min read
On this page
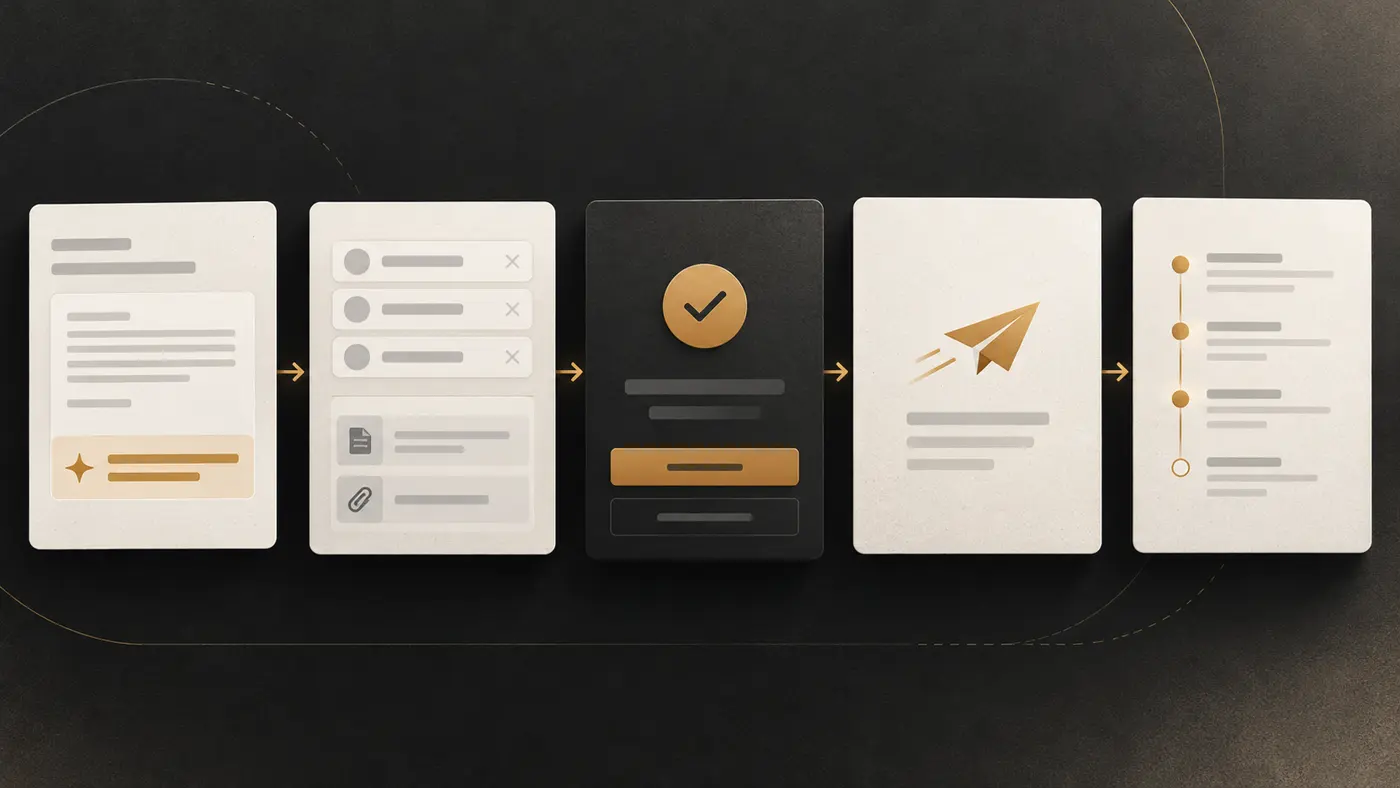
AI agents can help prepare client email safely, but a professional-services firm should not give them open-ended authority to send. The safer operating model is narrow permissions, human approval of the exact recipient, subject, body, and attachments, followed by a separate authorized send action. The firm should also keep a record that connects the approval to the content reviewed and define when approval can be revoked or the workflow must stop. This is a practical control model, not a promise of zero risk. It follows OWASP guidance that high-impact actions should require human approval and that downstream systems, rather than the language model, should enforce authorization (OWASP, “LLM06:2025 Excessive Agency”).
Can AI agents email clients safely?
Yes, if “email clients” means helping with bounded preparation and participating in a controlled workflow. No, if it means deciding what to send, to whom, and with which attachments without a meaningful human checkpoint.
That distinction matters in professional services because an email may carry a candidate profile, a client update, a proposal follow-up, or a meeting summary. The safe question is not simply whether an agent can produce an email. It is whether the firm can control the agent’s authority at every stage and show what a person actually approved.
OWASP describes Excessive Agency as a risk that can enable damaging actions when an LLM produces unexpected, ambiguous, or manipulated output (OWASP, “LLM06:2025 Excessive Agency”). Its email example points to read-only OAuth scope and/or requiring the user to review and manually hit send on every drafted email as mitigations (OWASP, “LLM06:2025 Excessive Agency”).
For a firm, that leads to a clear division of labor:
- The agent may classify incoming information, extract relevant details, or draft proposed text.
- An accountable person reviews the exact message package.
- Sending is a separate action taken only after that approval.
- The firm records what was reviewed, who approved it, and whether the approved content changed.
- Approval can be revoked, and defined conditions stop the workflow.
This is the practical meaning of human-in-the-loop work: the person is not merely present somewhere in the process. Their approval controls a specific consequential action.
What can an AI agent do before approval?
Before approval, the agent can assist with work that does not itself communicate with the client. A practical policy can allow three categories:
- Classify. Identify that an item appears to be candidate outreach, a client update, a proposal follow-up, or a meeting-summary draft.
- Extract. Pull proposed recipient details, discussion points, requested next steps, or referenced attachments into a reviewable package.
- Draft. Prepare a proposed subject and body for a person to assess.
The output remains a proposal. It should not become permission merely because the draft looks polished or because the underlying task appears routine.
For candidate outreach, the agent might prepare a message and identify the proposed recipient. For an M&A advisory update, it might turn approved working material into a client-facing draft. For consulting, it might draft a meeting summary with proposed next steps. For a proposal follow-up, it might prepare the subject and body and list the proposed attachment. In each case, the consequential boundary remains the same: preparation is not sending.
OWASP recommends minimizing extension functionality and avoiding open-ended tools where more granular functions can be used (OWASP, “LLM06:2025 Excessive Agency”). Applied as an operational control, that means giving an email assistant only the capability required for its current stage, rather than treating mailbox access as one broad permission.
What exactly should a human approve?
The reviewer should approve the complete message package that could leave the firm:
- Recipient: every To, Cc, and Bcc address.
- Subject: the exact subject line.
- Body: the exact text, including names, claims, requests, dates, and proposed next steps.
- Attachments: the exact set of files associated with the message.
The approval should apply to that combination, not to an abstract instruction such as “send the client an update.” If any component changes after review, our recommended control is to treat the prior approval as no longer sufficient and require a fresh review.
The person approving should also be accountable for the client communication. A visible approval button is not enough if the reviewer cannot see the final content or if the approved draft can be altered before the separate send action.
Pitstop is the workspace where your team and your AI agents run the firm together. Pitstop does not send or block email. Agents ask before anything leaves, a person approves the exact text, and the journal shows any gap. Its role in this model is to make the approval boundary explicit and reviewable.
Which controls reduce excessive agency?
Our recommended control model separates stages and gives each stage only the authority it needs. OWASP recommends minimum necessary permissions, tracking user authorization and security scope, and having downstream systems enforce authorization rather than relying on the LLM to do so (OWASP, “LLM06:2025 Excessive Agency”).
Here is our recommended workflow for a professional-services firm:
| Workflow stage | Allowed agent action | Human checkpoint | Stop condition |
|---|---|---|---|
| Intake | Classify the request and extract proposed message details | Confirm the task belongs in the client-email workflow | Recipient, purpose, or source material is unclear |
| Draft | Prepare a proposed subject, body, recipient list, and attachment list | Review the full message package | Draft contains an unresolved ambiguity or unsupported detail |
| Approval | Present the exact recipient, subject, body, and attachment set | An accountable person approves that exact package | Any element changes, approval is withheld, or approval is revoked |
| Send authorization | Make the approved package eligible for a separate send action | A person or downstream authorization control permits that action | Package does not match the approved version |
| Record | Bind the decision to the exact content reviewed | Confirm the journal reflects the decision and any gap | The approval, content, actor, or result cannot be connected |
This model creates several distinct controls:
- Narrow capability: drafting does not imply sending authority.
- Exact-content review: approval covers what would actually leave the firm.
- Separate authorization: the send action is not hidden inside drafting or approval.
- Content binding: the record connects the approval to a specific message package.
- Revocation: a person can withdraw approval before the send action.
- Stop rules: ambiguity, mismatch, or missing evidence halts the workflow.
These controls fit the client-service context described in Pitstop’s guidance for professional-services firms and its more specific work with executive-search teams.
When should the workflow stop instead of send?
A stop condition should be concrete enough that the team does not have to improvise at the moment of action. Our recommended policy is to stop when:
- The intended recipient or any copied address is uncertain.
- The subject or body differs from what the person approved.
- An attachment is missing, added, replaced, or changed after approval.
- The draft contains an unresolved ambiguity, placeholder, or unsupported detail.
- The approver rejects or revokes the decision.
- The proposed send action cannot be tied to the approved message package.
- The journal reveals a gap between the review and the action.
Stopping does not mean the agent has failed. It means the control worked. The workflow can return to drafting, ask a person to resolve the ambiguity, or seek a new approval for the corrected package.
Revocation belongs in the model because approval is not the same event as sending. If circumstances change between those steps, the accountable person needs a way to withdraw the authorization. A practical policy should specify that revocation remains effective until the separate send action occurs and that any later attempt requires a current approval.
How should a firm record the decision?
The record should answer a simple question: can the firm connect the human decision to the exact content that was eligible for the send action?
Our recommended record includes:
- The accountable reviewer.
- The approval or rejection decision.
- The time of that decision.
- The exact recipient fields, subject, body, and attachment set reviewed.
- Any later change, revocation, or renewed approval.
- Whether the separately authorized action matched the approved package.
The important property is binding. A log line that says “approved email” is weak if the final message cannot be compared with what the person saw. The record should make a mismatch visible rather than asking the team to trust that nothing changed.
This approach also gives operations leads a usable review point. They can inspect whether the process followed the firm’s own policy, identify a gap in the journal, and correct the workflow. Teams defining the broader boundary can use an AI acceptable use policy for professional services alongside message-level controls.
What else should firms know about AI agent email?
Can an AI send an email?
An AI system can participate in a workflow that results in an email being sent. For client communication, our recommendation is to limit the agent to preparation, require approval of the exact message package, and keep sending as a separate authorized action. OWASP’s email example identifies read-only OAuth scope and/or user review with a manual send action for every drafted email as mitigations (OWASP, “LLM06:2025 Excessive Agency”).
Is reviewing the body enough?
No. The same body can create a different action when the recipient, subject, or attachments change. The reviewer should see and approve the exact recipient fields, subject, body, and attachment set together.
Can a firm pre-approve a category of routine emails?
A category can help classify work, but it should not replace exact-message approval under this control model. “Proposal follow-up” describes a type of task. It does not approve a particular recipient, claim, attachment, or final text.
What happens if the message changes after approval?
Our recommended control is to invalidate the earlier approval and return the changed package for review. The new decision should be bound to the new version.
Does human approval remove all risk?
No. This model reduces the authority delegated to the agent and creates a clear checkpoint, but it is not a claim of zero risk. OWASP says high-impact actions should require human approval before they are taken and that authorization should be enforced in downstream systems, not by the LLM (OWASP, “LLM06:2025 Excessive Agency”).
The practical standard is straightforward: let agents help prepare the work, let an accountable person approve exactly what could leave, keep sending separate, and preserve a record that exposes any gap.
Written by Loïc Guyon (Tileo), operator of Pitstop.